


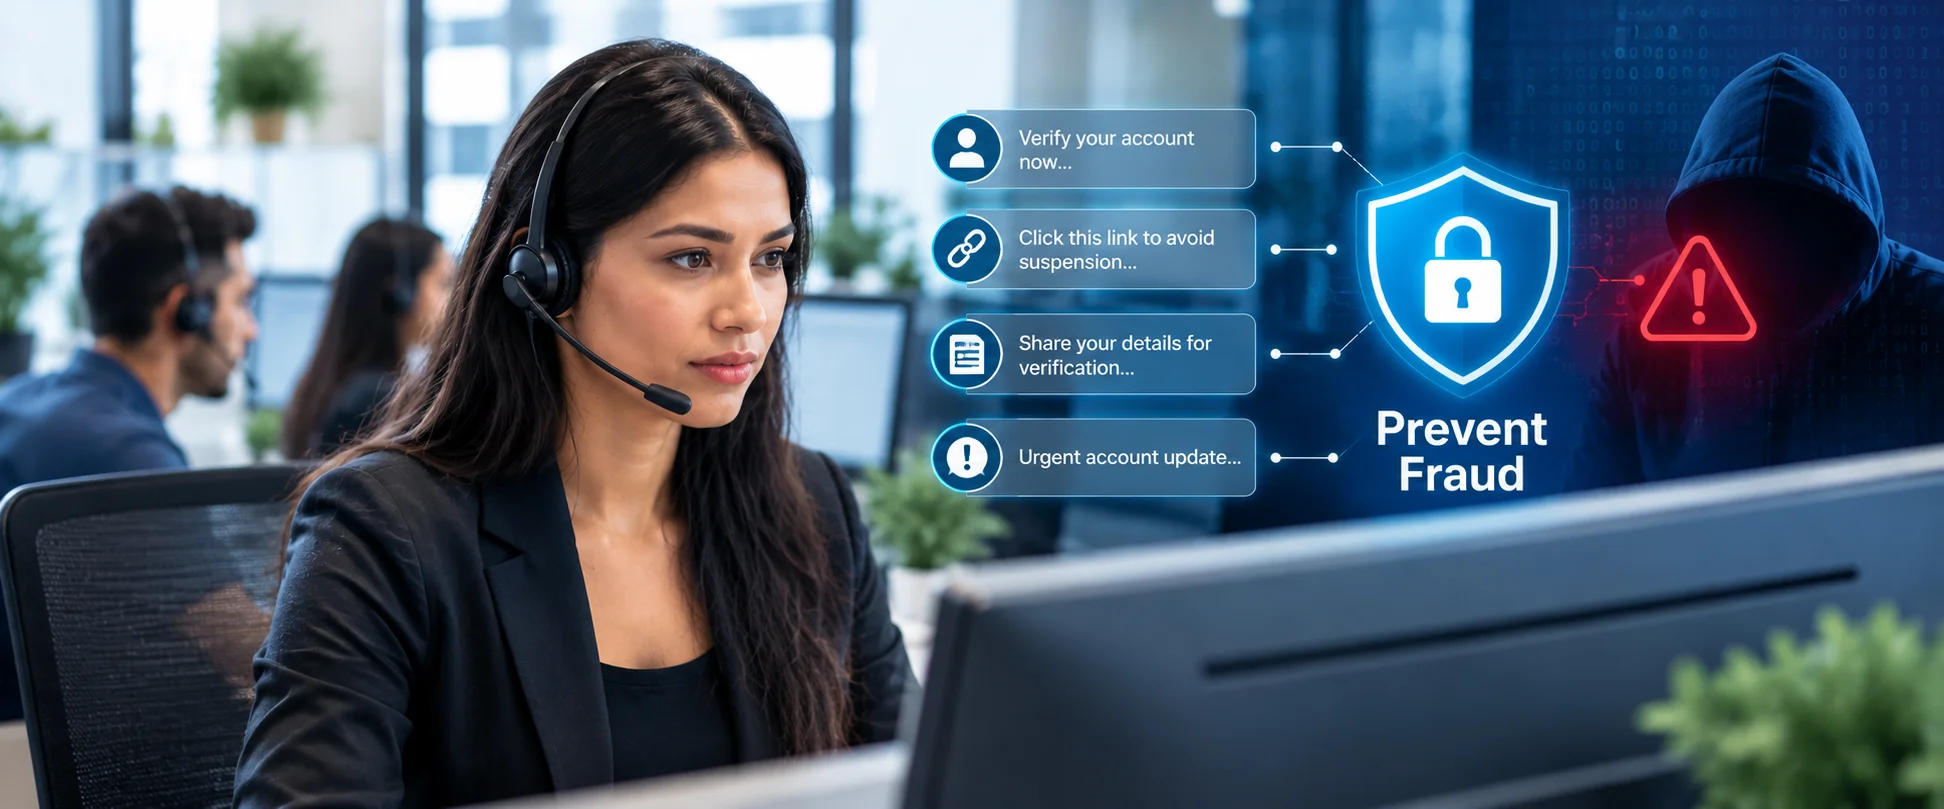

Picture a fraudster who never picks a lock or writes a line of malicious code. Instead, they dial a support line, sound a little rushed, and ask a tired agent for “just one quick favor.” That single phone call can undo years of firewall investment. Retail brands rarely ask this question early enough in vendor selection: is our support desk secure, or just polite? That gap sits at the center of retail contact center fraud prevention. It starts with a conversation, not a hack.
Retailers have spent a decade hardening checkout pages and point-of-sale terminals. Meanwhile, fraudsters simply walked around that wall and knocked on the customer support door instead. Contact centers reward speed, warmth, and quick resolution, and criminals exploit exactly those instincts. This is precisely where contact center fraud prevention retail leaders need to focus next. The attack surface has quietly shifted from the network to the phone line.
Why Retail Customer Support Teams Became the Favorite Target
Pindrop’s 2023 Voice Intelligence and Security Report found something striking. Large retailers face a fraud rate of roughly 1 in 99 inbound calls, seven times higher than banking’s 1 in 749. Retail is exposed because agents handle stored payment methods, loyalty balances, and shipping details constantly. Popular, easily resold products make the incentive even stronger for organized fraud rings.
Three Different Numbers, One Overlapping Problem
It helps to separate what is actually being measured before stacking statistics together. Contact center exposure describes fraud attempts against the voice and chat channel itself, like Pindrop’s 1-in-99 figure above. Account takeover exposure describes compromised customer accounts instead. Fraud-consortium research from CIFAS reported millions of confirmed cases across 2024 alone. Retail loss exposure covers the financial fallout on top of that. The National Retail Federation estimates that e-commerce return fraud costs US retailers roughly $23 billion annually.
These three categories overlap constantly, and that overlap is the real story. A contact center interaction is often where fraudsters gather or verify stolen data first. UK Finance’s own fraud researchers describe contact centers as handling the early “data-gathering” stage of fraud. That stage happens well before any transaction shows up on a statement. In other words, the phone call is rarely the whole crime. It is usually the reconnaissance mission that makes the bigger theft possible later.
The Anatomy of a Social Engineering Customer Service Attack
Social engineering customer service attacks rarely look dramatic from the agent’s chair. Most sound like an ordinary, slightly stressed customer. Understanding what fraudsters actually want helps agents recognize the pattern faster than memorizing a generic script ever could.
Identity and account takeover remains the most common goal here. A caller pushes an agent toward resetting a password or changing an email on file. Refund manipulation follows closely behind that pattern, with fraudsters claiming a missing or defective order. The aim is always the same: pressure an agent into an unearned reimbursement. Loyalty point theft targets rewards balances directly, since points convert to cash or merchandise easily. Gift card fraud works similarly, coaxing an agent into issuing, replacing, or transferring stored value. Internal impersonation flips the script entirely. Here, a caller poses as a supervisor, an IT technician, or even a fraud investigator. Their goal is simple: pressure an agent into bypassing normal controls altogether.
Why Well-Trained Agents Still Get Fooled
Skilled agents get fooled because social engineering exploits ordinary workplace instincts, not technical ignorance. Fraudsters research targets on LinkedIn and social media first, then reference real details that sound authentic. Handle-time pressure and unclear verification rules make the right call harder in the moment. Fragmented customer data adds another layer of difficulty on top. As Pindrop’s David Dewey once put it, “It’s a wild west out there.” That line still holds up, arguably more than ever, now that AI-generated voices sound eerily natural.
A Real-World Case Retail Leaders Should Study
The 2023 MGM Resorts breach offers a sobering lesson, even though MGM operates in hospitality rather than pure retail. The relevant takeaway isn’t the casino setting. It is the attack path itself: public employee research, a support interaction, a credential reset, and a costly shutdown. CISA’s advisory on the group known as Scattered Spider explains the pattern well. Attackers routinely combine phone-based impersonation with help-desk pressure to bypass identity checks entirely.
MGM’s own regulatory filing with the SEC estimated the incident’s negative impact at roughly $100 million. Additional one-time remediation costs pushed the total even higher. MGM’s CEO, Bill Hornbuckle, later told reporters plainly, “It was partially socially engineered.” Nothing about that breach required advanced hacking skill. It required patience, confidence, and one under-trained conversation. That is exactly the exposure retail brands carry every busy season, especially when temporary staff handle resets under pressure.
Building Retail Customer Support Security Into Everyday Operations
Strong retail customer support security works best as layers rather than a single checkpoint. Identity verification should combine more than static knowledge-based questions, since personal data already sits exposed from prior breaches. Interaction intelligence adds a second layer, watching for unusual combinations like a rapid address change followed by a large reorder. Agent controls matter just as much here. Frontline staff need clear escalation paths and explicit permission to pause a rehearsed-sounding call. Quality monitoring at scale forms a fourth layer, reviewing far more conversations than a small manual sample ever could. A feedback loop closes the system last. Confirmed fraud patterns should feed straight back into training, scripts, and authentication rules.
Consistency across departments matters as much as the framework itself. A brand’s 24/7 retail customer service team needs the same verification rules as everyone else. So does its order tracking and fulfillment workflow, and its returns and refund processing desk. Fraudsters actively search for the weakest linked process, so gaps between teams become an open invitation.
Where Technology Fits, Without Overselling It
Automated quality monitoring can evaluate a far larger share of customer conversations than manual sampling ever allowed. That coverage helps fraud teams spot recurring verification failures sooner. ServeRetail applies this approach through its AI-QMS platform, which audits conversations at a scale most spot-check programs cannot match. AI-enabled voice workflows offer a similar advantage. They can build authentication rules and behavioral signals directly into a call. ServeRetail’s AI Voice Agent works the same way, routing unusual patterns to connected monitoring systems for human review. Technology narrows the gap considerably, though it still works best alongside trained judgment, not in place of it.
A Quick Gut-Check Before You Choose a Support Partner
A few honest questions reveal more than any vendor pitch deck. Start with identity: how does customer verification actually work, and do high-risk requests trigger stronger checks automatically? Move next to agents, since staff need room to escalate a suspicious call without fear of hurting their handle-time score. Technology deserves scrutiny too, particularly whether quality monitoring covers a meaningful share of conversations rather than a token sample. Workflow consistency matters just as much, so ask whether refund, address-change, and password-reset processes follow identical rules across every channel. Governance closes the loop, and the honest question is whether confirmed fraud incidents feed back into training within weeks rather than quarters. Vendor fit deserves its own scrutiny, too. Reviewing real retail BPO case studies tells you more than generic customer service claims ever will, since retail-specific fraud patterns rarely match what a telecom or healthcare-focused BPO has already solved.

Your contact center is not simply where customers ask for help. It is where customers prove who they are, request money back, and regain access to valuable accounts. Every verification step is quietly part of your fraud-control architecture, whether anyone labels it that way or not.
Fraud will keep evolving as generative AI makes impersonation cheaper every year. Retail brands that treat their support desk as a strategic security asset gain a real edge. They absorb these attacks with far less damage than competitors who still treat support as a cost center. If you’re ready to pressure-test your own program, ServeRetail’s retail-trained agents and layered monitoring were built exactly for this challenge. Book a free consultation and find out where your real exposure sits before a fraudster finds it first.


